PHP2Shell: what happened this week and how we protected Junovy
A critical flaw in PHP made the news this week. Here's what it is, what we did on the same day, and what to ask if your own website runs on PHP.
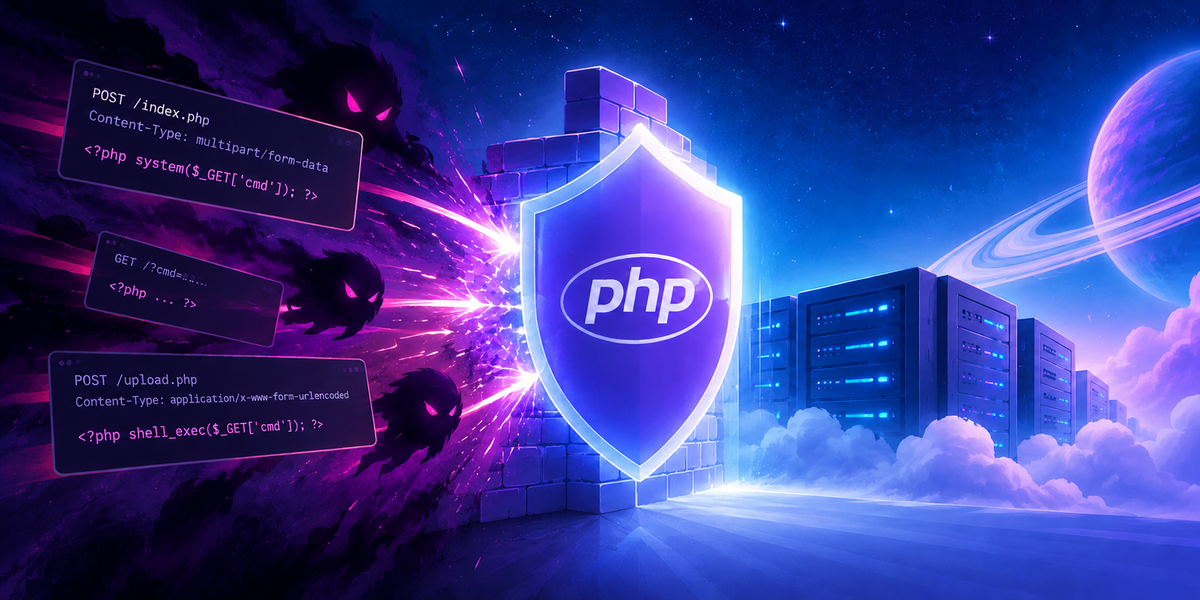
On Wednesday 21 October, the PHP team released fixes for two serious security flaws, nicknamed PHP2Shell. PHP is the programming language behind a huge part of the web, from WordPress sites to webshops to the software that runs Junovy Cloud.
We've already emailed every Junovy customer directly. This post is the public version: what happened, what we did about it, and what you can check if you run a website of your own.
🔍 What happened
The two flaws could let an attacker run their own code on a web server without logging in. European and UK security agencies (CERT-EU and the NCSC) rated them as critical, and there were early reports of attacks within hours.
The problem is in PHP itself, not in any one app built on it. That's why it affects so many websites at once, and why the fix has to happen on the server, not on your laptop or phone.
🛡️ What we did the same day
Within hours of the announcement we had protection in place on Junovy Cloud (including Talk and Office) and on our support site. Every known way of exploiting these flaws relies on one particular kind of web request, so we blocked that kind of request at the front door before it could reach the software behind it.
We also checked every service we run to find out which ones use PHP at all. Only two do, and both are covered.
Then we checked our systems for any sign that someone had tried their luck before the protection went in. That first check found nothing unusual. We'll run it again once the permanent fix is installed.
⏸️ What's paused for now
Blocking that kind of request has a side effect: a few upload features are paused until the fix is in.
- Adding attachments to Boards cards, Mail and Forms straight from your computer
- Changing your profile picture
- Uploading a logo or background in your Cloud's appearance settings
Everything else works as normal: logging in, your files and the sync apps, uploading files in Junovy Cloud, Talk chats and calls, editing in Junovy Office, and your calendars, contacts and tasks.
If you need to attach something in the meantime, upload it to your Junovy Cloud files first and then attach it from Files.
🔧 What's next
Once the fixed version of PHP is ready for our setup, we'll install it and switch the paused features back on. Our customers will get a short email from us when that's done, and we'll update this post too.
💡 If your website runs on PHP
If you have a WordPress site, a webshop or any other website on PHP, it's worth sending your web host or developer one quick question: "Has PHP been updated to a version with the PHP2Shell fix?" The fixed versions are 8.5.12, 8.4.27, 8.3.36 and 8.2.35, or newer.
And keep an eye out for scam emails. Big security stories bring a wave of fake "urgent" messages. We'll never ask for your password by email or send you a link to "verify" your account.
For the technically curious, the flaws are CVE-2026-109618 and CVE-2026-109619. The CERT-EU advisory and the NCSC's write-up have the details.
🤝 Questions?
If you're a Junovy customer and something isn't working the way it should, just reply to our email or get in touch. If you're wondering whether your own setup is affected and don't know who to ask, get in touch too; we're happy to point you in the right direction.
Less busy work, more business.
Junovy provides European cloud hosting and business software for small businesses and communities. Built on open-source foundations with privacy at the core. Learn more at junovy.com.